Threat Visibility and Security Analysis

Lighting the Dark Spots: Threat Visibility and Security Analysis in Cyber Defense

Threat Visibility and Security Analysis

Modern enterprise networks grow more complex and fragmented every day, with thousands of endpoints, hybrid cloud environments, SaaS applications, and a remote workforce. This complexity creates unique hiding places for attackers and brings security teams their greatest fear: visibility blind spots.

The most dangerous misconception in cybersecurity is the idea that "we are not receiving any alerts from our systems, so we are safe." Advanced persistent threats (APT) and modern ransomware can quietly exfiltrate data for months behind traditional firewalls without triggering a single alert. The basic rule of cyber defense today is clear: you cannot stop a threat you cannot see, and you cannot manage a risk you cannot analyze.

As Assista, we do not only offer organizations reactive protection tools. We build Advanced Security Analytics architectures that give cyber visibility down to the deepest capillaries of the infrastructure and detect threats while they are still forming.
Where Traditional Security Monitoring Falls Short

Many organizations still rely on systems focused only on log collection (SIEM) or on traditional antivirus logic. These reactive approaches create the following blind spots in today's threat landscape:

  • Data Left in Silos

    When network traffic data, endpoint logs, and cloud activity are not correlated, following an attacker's footprints becomes impossible.

  • Alert Fatigue

    Security tools producing thousands of low-quality alerts a day cause analysts to miss the real and critical threats.

  • Lack of Behavioral Analysis

    When attackers use legitimate user identities or system tools (Living off the Land), signature-based security software cannot recognize these abnormal behaviors as a cyber threat.

Proactive Threat Visibility and Security Analytics Engineering with Assista

At Assista, we take an X-ray of your infrastructure to protect your digital assets and design an AI-supported, unified visibility ecosystem:

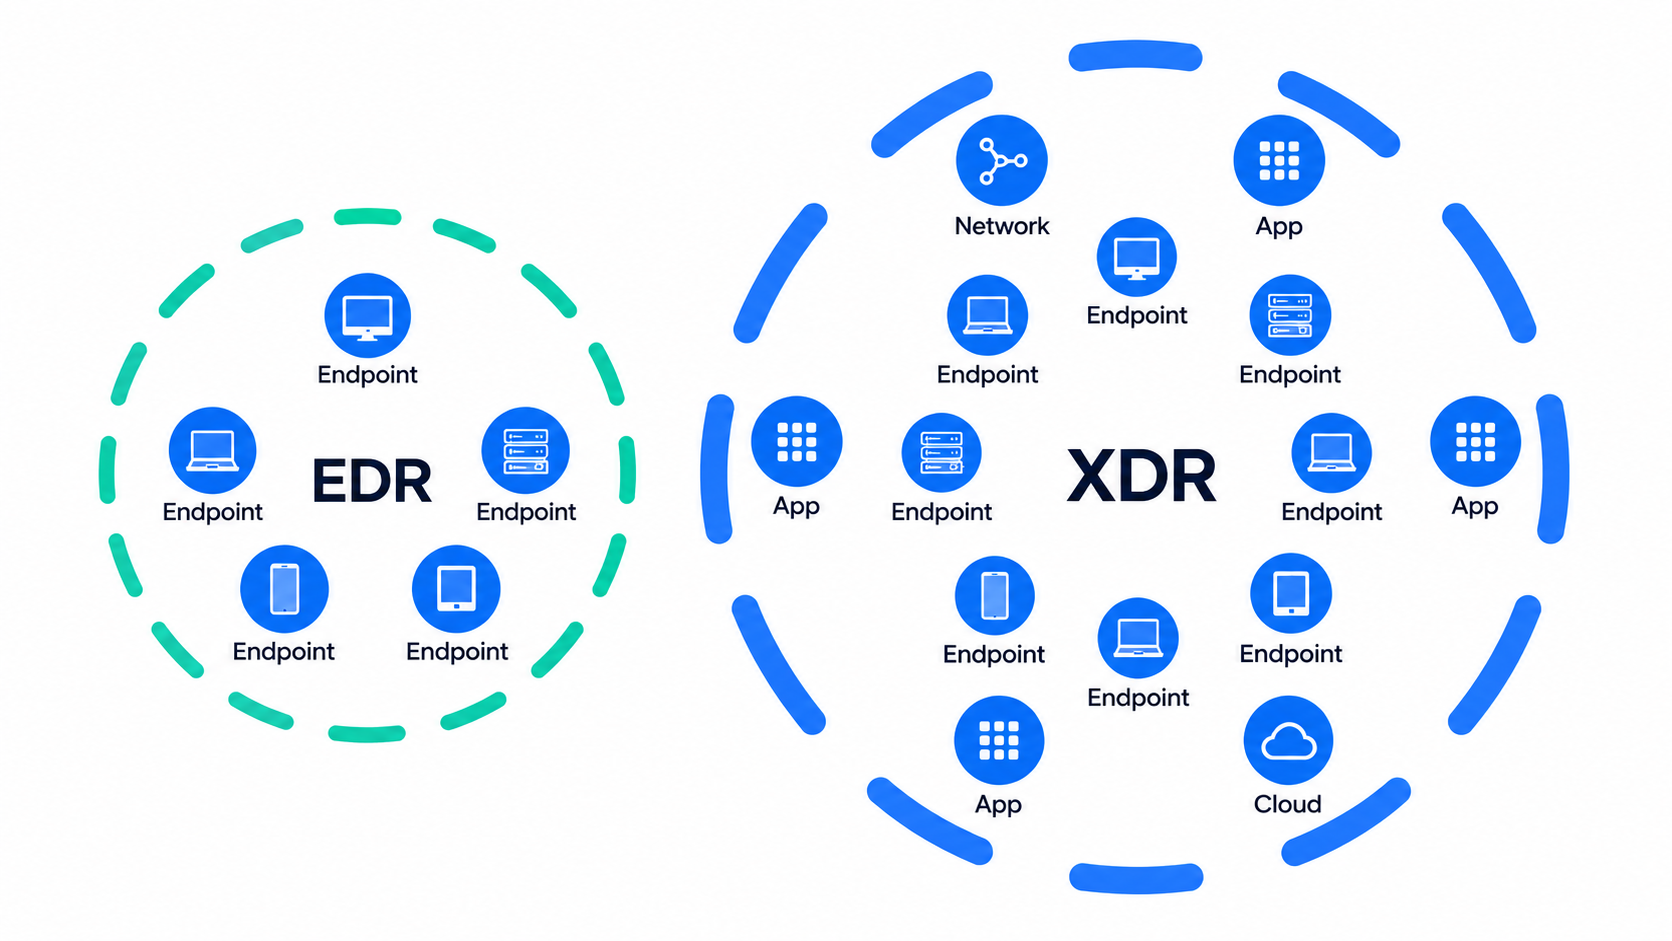
Endpoint Behavior Analysis and Threat Hunting (EDR / XDR)

Endpoint Behavior Analysis and Threat Hunting (EDR / XDR)

  • We do not only watch attack logs. We deploy EDR/XDR (Endpoint/Extended Detection and Response) architectures that analyze every process running on user computers and servers, movements in memory (RAM), and registry changes in real time. We isolate threats at the endpoint before they spread across the network, and we apply proactive Threat Hunting methods.

Light Up Your Blind Spots with Assista Expertise

Threat visibility and security analysis cannot be solved only by installing software; it requires deep correlation logic, cyber threat intelligence integration, and architectural engineering. Assista's expert team, holding top global certifications in cybersecurity architecture, analyzes your organization's cyber visibility maturity (SOC Assessment) and draws the right visibility map.

To remove the cyber blind spots in your infrastructure, bring your threat detection times (MTTD) down to minutes, and build a proactive cyber defense line, contact the Assista team.